Weekly Cyber Briefing 16.10.2026
Weekly Cyber Update: 16 October 2026
Ahold Delhaize takes systems offline; French supermarkets feel the heat; and extortionists target shipping and logistics firms
Weekly Cyber Briefing 16.10.2026
Ahold Delhaize takes systems offline; French supermarkets feel the heat; and extortionists target shipping and logistics firms
On Sunday, retail giant Ahold Delhaize found a security issue on its network and deliberately took systems offline to contain it. The group owns brands including Delhaize, Albert, bol, Etos and Gall & Gall in Europe, and Food Lion, Stop & Shop, Giant Food and Hannaford in the US. It reported 2024 net sales of over $104bn (£78bn).
Let’s put this into context. Albert Heijn has around 38% of the Dutch grocery market, making this incident bigger than if Tesco shut down. In the Netherlands, this is huge.
Commendably, the CEO came out publicly, owning the media messaging and estimating a full restoration would take “a few days to a week”. We are already seeing restorations happen. It doesn’t appear that customer, employee or third-party data was stolen and no group/threat actor has come forward. However, the impact was significant:
Albert Heijn hasn’t said, but a little is known from leaks and commentary.
Dutch broadcaster NOS reported that Albert Heijn identified servers in the US, Poland, Moldova and Turkey used in the attack. NOS stressed this says nothing about where the attackers are, since traffic is easily routed through other countries.
Albert Heijn’s investigation also suggests servers belonging to Ahold Delhaize’s US business may be involved, according to Dutch News.
This is not the group’s first incident. INC Ransom stole personal, financial and health information on more than 2.2 million people in a November 2024 attack on Ahold Delhaize’s US systems, according to Bleeping Computer.
NIS2 came into force in the Netherlands in August and covers food businesses engaged in wholesale distribution and industrial production. Ahold Delhaize’s distribution operations are therefore the likely route into scope, rather than its stores. If it is in scope, it would have informed the regulator within 24 hours.
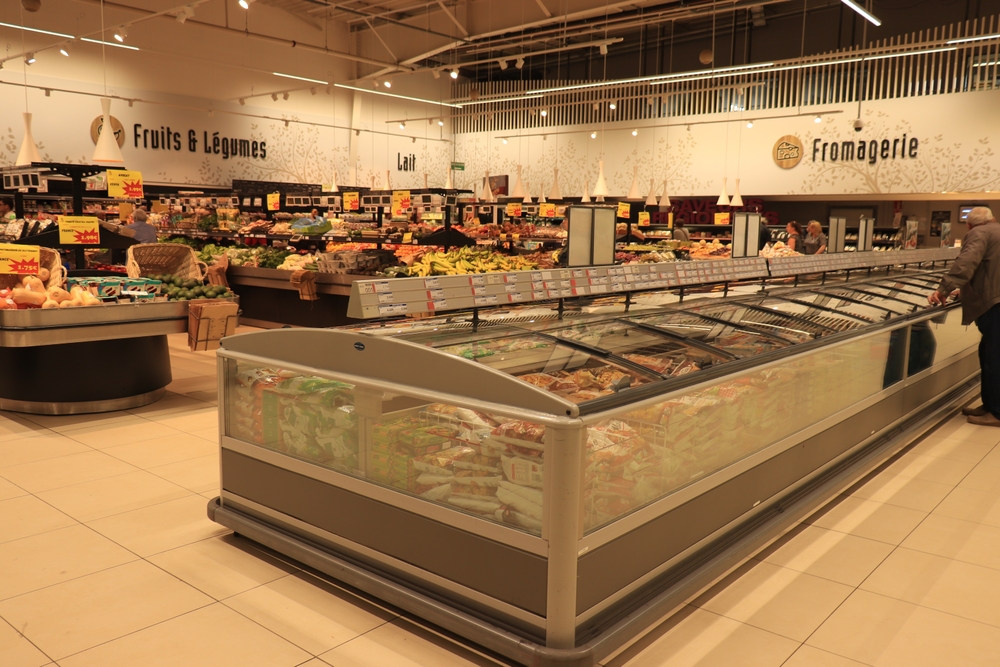
French supermarkets nationwide have been hit in a coordinated attack targeting operational technology (OT). Overnight on 11 to 12 October, attackers took control of refrigeration controllers at hundreds of stores and forced fridges and freezers to defrost, spoiling food and causing fires. According to The Hacker News, the impact spanned:
The French government has since put the total at around 700 supermarkets. The head of Les Mousquetaires expects losses of tens of millions of euros across France. The Paris prosecutor’s cybercrime office has opened an inquiry. The attack may not be limited to France. Sekoia’s Félix Aimé told Reuters that Spain, Portugal, Poland, Germany and Belgium were also affected.
Each store has one supervisory controller that runs all its refrigeration. These control panels can be reached over the internet so maintenance companies can adjust them remotely. According to BFMTV, the attackers hijacked the automatic defrost function, replacing the normal cycle of about two hours a day with a continuous forced defrost set to 50°C. This hit:
A researcher on X (formerly Twitter) has publicly reconstructed the suspected exploit chain, with a proof of concept and detection rules, although officially, the route in is not established. As of 13 October, CERT-FR had named no vulnerability, no firmware version and no entry route. The prime suspect is a hidden “code of the day” login according to The Hacker News.
Synacktiv documented a date-derived authentication bypass on the AK-SM 800 and AK-SC 255 in May 2023. Because the products are end of life, it was never fixed.
On the newer 800A, Claroty Team82 found the application would accept a generated daily code instead of the administrator password. They rebuilt the generation algorithm, which means an attacker could calculate a valid code for any day.
CVE-2025-41450 was fixed in version 4.2. A second flaw, CVE-2025-41451, allows command injection leading to remote code execution and was fixed in 4.3.1. French scanning firm Onyphe said only a small minority appeared to be running the latest software, suggesting updates aren’t necessarily being made.
It’s possible devices were discovered with services like Shodan and then attempts made to gain access with default device passwords. Predicta Lab counted 2752 Danfoss systems exposed online on Monday, 1590 of them in France. Shodan tracks over 4500.
This has implications for the EU’s other headline cyber regulation. The Cybersecurity Resilience Act (CRA) has required security notifications since 11 September 2026, regardless of when a product was placed on the market. Manufacturers must notify ENISA and the coordinating national CSIRT of any actively exploited vulnerability through the Single Reporting Platform within 24 hours.
If an exploited vulnerability is confirmed in Danfoss, Copeland or Dixell products, this is among the first major real-world tests of that duty.
Products placed on the market before December 2027 are exempt from the CRA’s design rules, but remain subject to reporting while they are available on the EU market.
Looking ahead, hidden daily login code is exactly what the CRA’s secure-by-default requirements are meant to eliminate from new products from December 2027. However, this doesn’t require improvements for old controllers already online.
On 12 October, the n0n extortion group added 38 port, shipping and logistics organisations to its leak site in one batch. Ransom demands range from $2.4m (£1.8m) to $14m (£11m) and don’t scale with data volume. The full list is on SOCRadar and on ransomware.live under 12 October. None of the named organisations has admitted an incident so far.
The victims span 18 countries and almost every link in the container supply chain: terminal operators, shipping lines, port IT and EDI providers, agencies and logistics firms. South Korea accounts for 12 entries while BMT IQ is the only UK organisation listed. It apparently had 90MB of data stolen across 18 files: commercial e-invoices, equipment interchange receipts and inspection records.
Some reports have pointed to infostealer logs as the way in. That is based on n0n’s known methods, not evidence from this campaign. SOCRadar currently disputes the theory, finding no stolen-credential matches for many of the maritime victims. We can attempt deduce a theory based upon the fact that:
The large blast radius points the same way: an exposed shared application or vulnerability, and a possible supply chain incident. SOCRadar compares the pattern to the MOVEit and Cleo mass-exploitation campaigns, while noting no evidence links n0n to either. However, there is a possible link to maritime software provider CyberLogitec, according to Cydome. There is some circumstantial detail that fits:
Features 13.10.2026
The Dutch Institute for Vulnerability Disclosure (DIVD) is not used to being the story
Features 09.10.2026
The job of the firm’s first responders just got a whole lot harder